Configure Google Cloud KMS for CMEK
Use Google Cloud KMS to provide an encryption key for your organization.
claude "/claude-api help me configure a customer-managed encryption key with Google Cloud KMS"This guide walks through configuring a Google Cloud KMS key as a customer-managed encryption key (CMEK) for your Anthropic organization.
Prerequisites
- A Google Cloud project with billing enabled.
- The Cloud KMS API enabled (
cloudkms.googleapis.com). - Permissions to create KMS key rings and keys, and to set IAM policy on them (
roles/cloudkms.adminor equivalent). - An Anthropic Admin API key for your organization.
- The
gcloudCLI installed and authenticated. - Cloud KMS Data Access audit logs enabled for the project (IAM & Admin > Audit Logs > Cloud Key Management Service, with
DATA_READandDATA_WRITE). These are off by default; without them, Anthropic's encrypt and decrypt operations produce no entries in Cloud Logging.
Anthropic service account email
To have Anthropic use your encryption key, you must give Anthropic's service account a key it can use for encrypting data. The service account email for Anthropic CMEK is:
anthropic-cmek-client-us@gcp-anthropic-cmek-clients.iam.gserviceaccount.comEncryption key setup
Create or choose a key ring
Skip this step if you already have a key ring to reuse. Key rings are regional. Choose a single-region US location such as
us-east5that matches the Anthropic geography you are configuring. Multi-region locations likeusandglobalare not supported.gcloud kms keyrings create <your-keyring-name> \ --project=<your-project-id> \ --location=<region>Create the crypto key
Create a symmetric key with the
ENCRYPT_DECRYPTpurpose. Anthropic strongly recommends HSM protection: Cloud KMS HSM keys are FIPS 140-2 Level 3 validated, and the cost delta over software keys is small.gcloud kms keys create <your-key-name> \ --project=<your-project-id> \ --location=<region> \ --keyring=<your-keyring-name> \ --purpose=encryption \ --protection-level=hsmFor software protection instead, omit
--protection-level=hsm. Nothing else in this guide changes.You can also create the key from the Google Cloud Console. Open the key ring, click Create key, select Generated key, set the purpose and algorithm to symmetric encrypt and decrypt, and choose HSM under protection level.
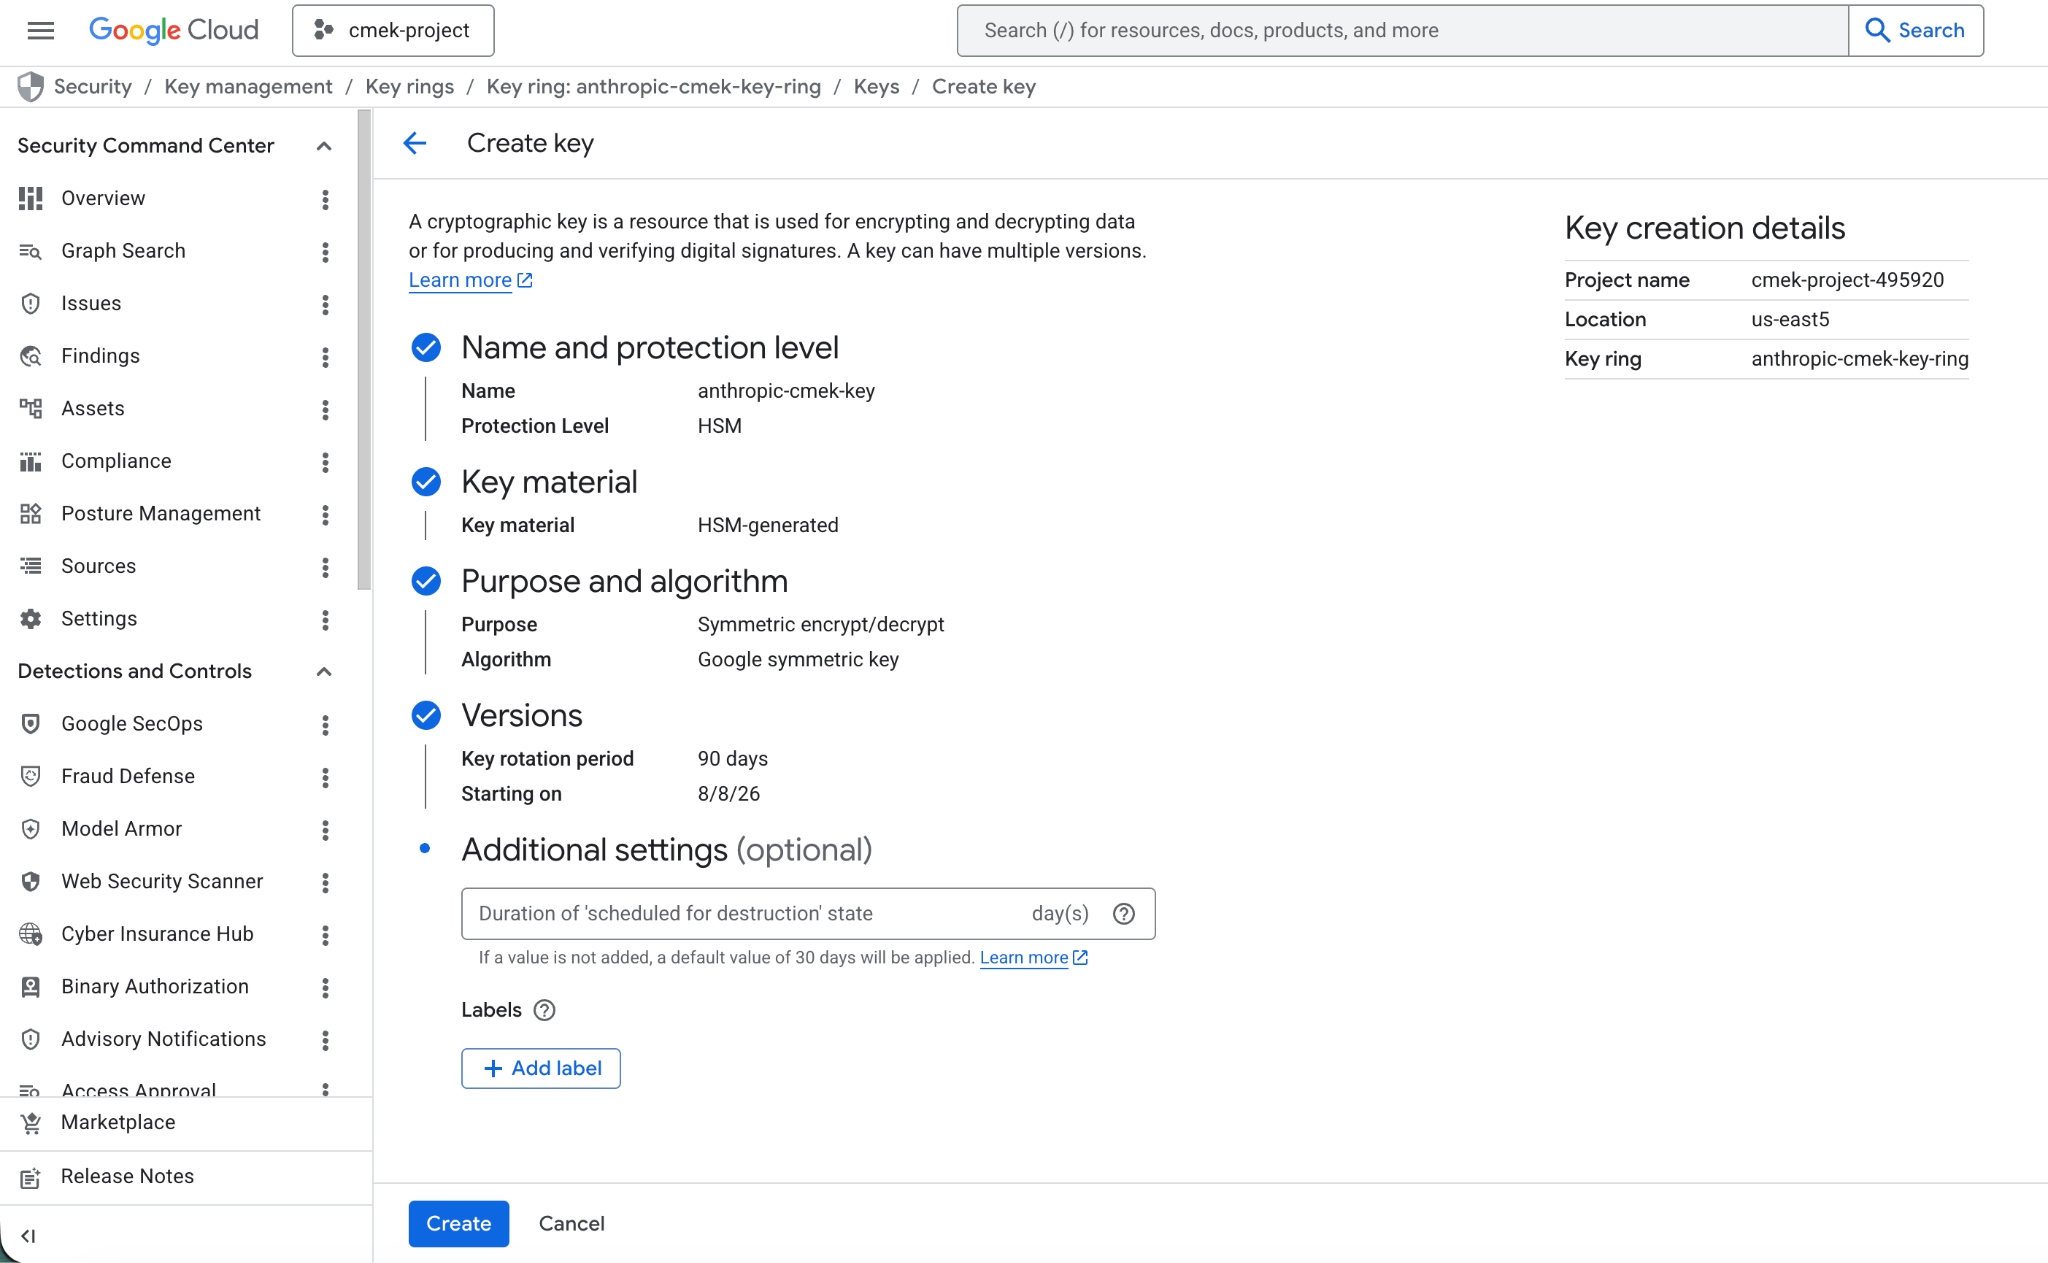
Create an HSM-protected symmetric encrypt/decrypt key. Grant Anthropic's service account access to the key
Two key-level IAM bindings are required. Both are scoped to the single crypto key, not project-wide or keyring-wide.
Encrypt and decrypt, which Anthropic uses to encrypt and decrypt the data keys that protect your workspace data (envelope encryption):
gcloud kms keys add-iam-policy-binding <your-key-name> \ --project=<your-project-id> \ --location=<region> \ --keyring=<your-keyring-name> \ --member="serviceAccount:anthropic-cmek-client-us@gcp-anthropic-cmek-clients.iam.gserviceaccount.com" \ --role=roles/cloudkms.cryptoKeyEncrypterDecrypterViewer, for the metadata read (
cryptoKeys.get) Anthropic performs at startup to validate the key's purpose and algorithm:gcloud kms keys add-iam-policy-binding <your-key-name> \ --project=<your-project-id> \ --location=<region> \ --keyring=<your-keyring-name> \ --member="serviceAccount:anthropic-cmek-client-us@gcp-anthropic-cmek-clients.iam.gserviceaccount.com" \ --role=roles/cloudkms.viewerFrom the Console, select the key, open the Permissions panel, click Grant access, and add the service account with both the Cloud KMS CryptoKey Encrypter/Decrypter and Cloud KMS Viewer roles. Make sure you are on the key's permissions page, not the key ring or project, so the grant is scoped to this key only.
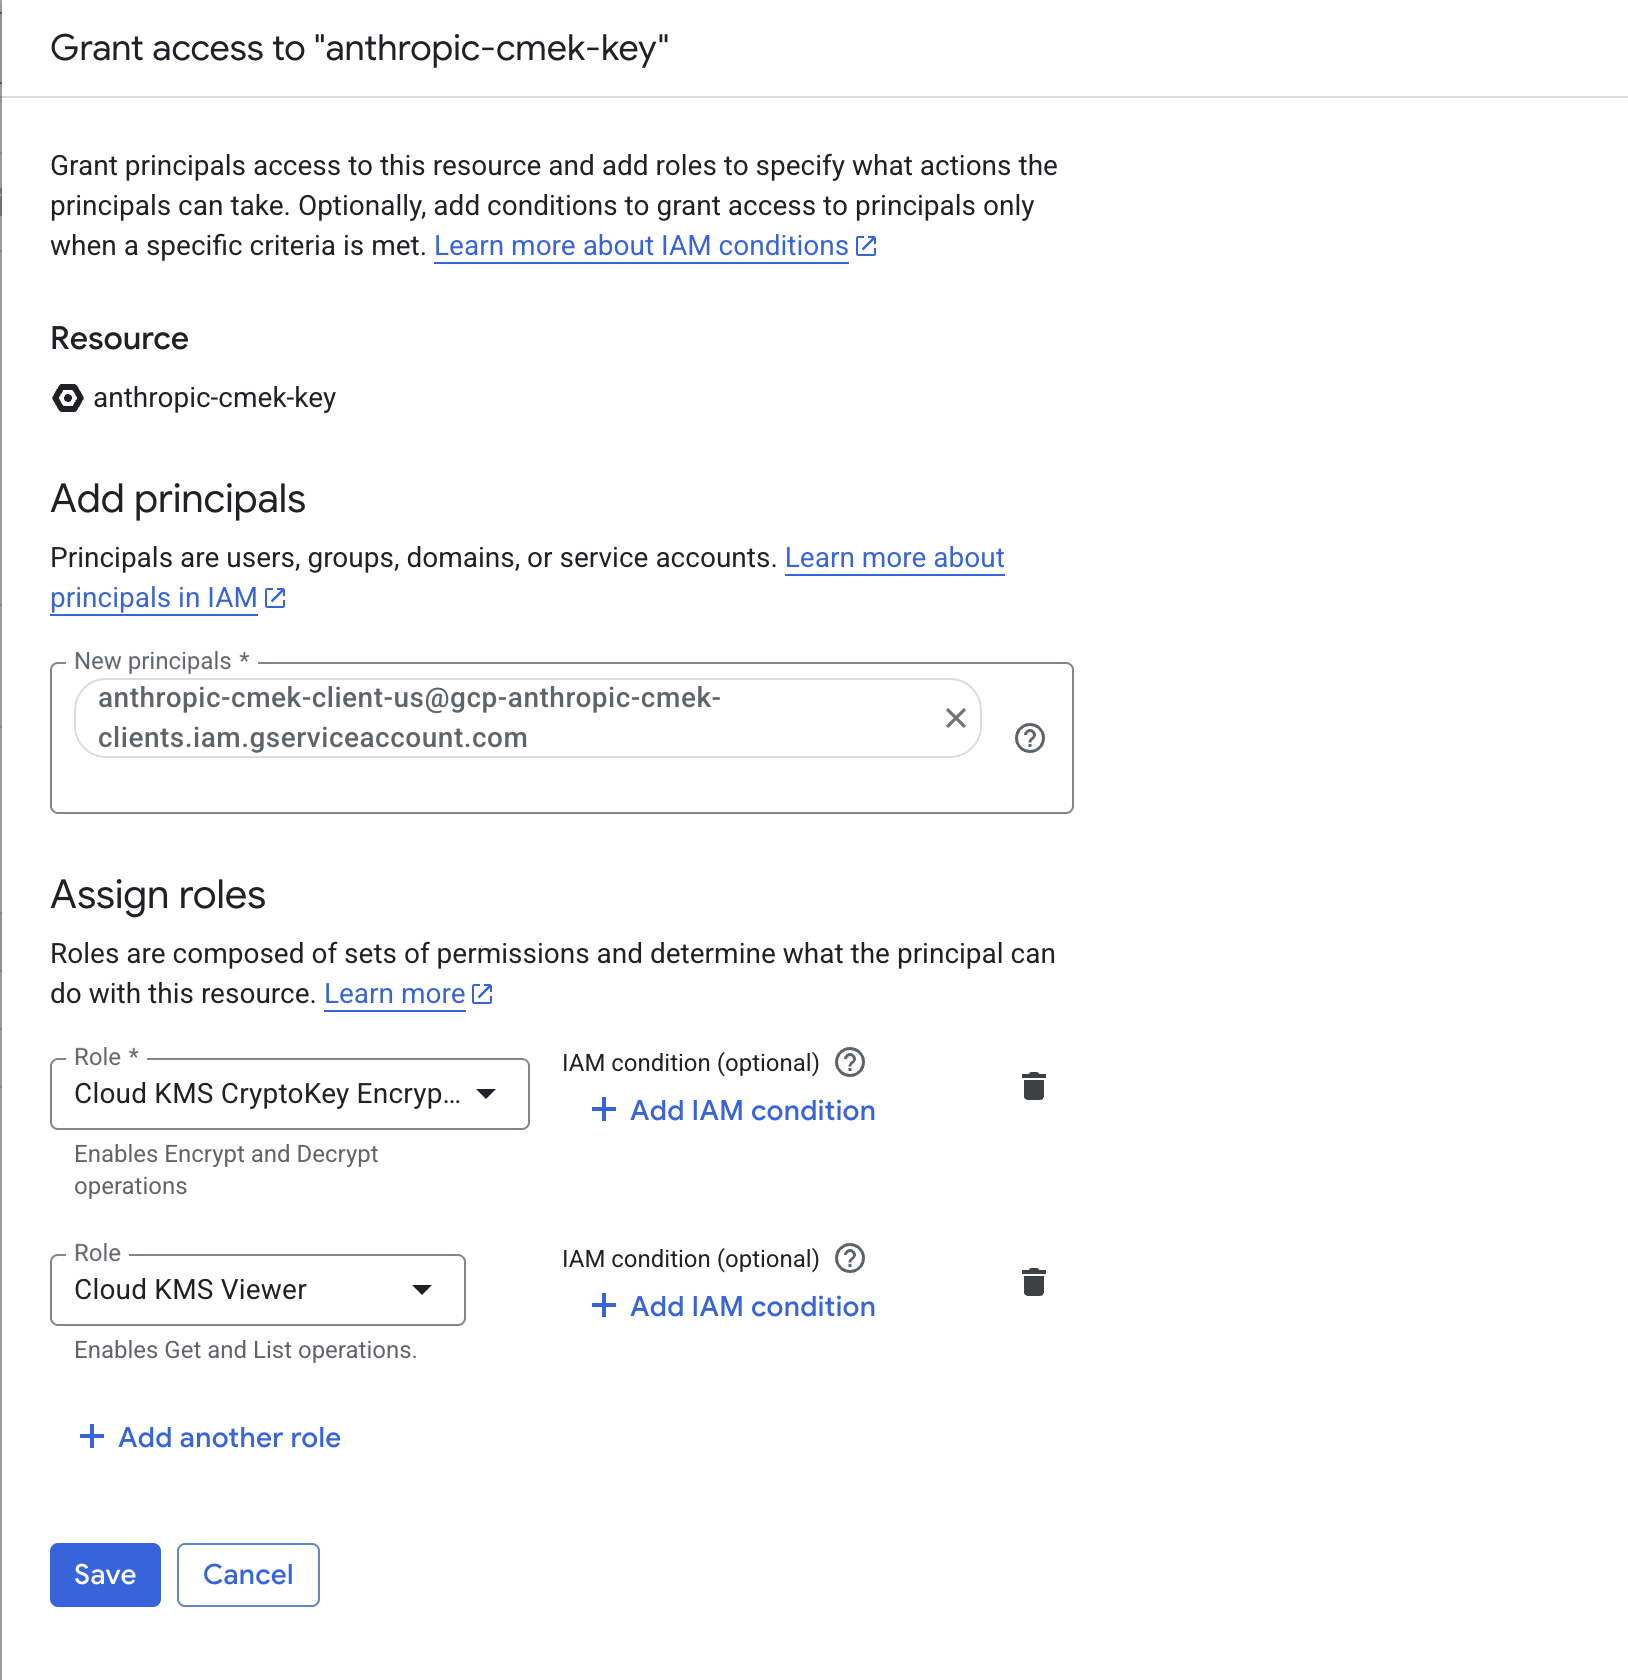
Grant the Anthropic service account both roles, scoped to the key. Note the full key resource name
You pass this to Anthropic when you register the key. The format is:
projects/<your-project-id>/locations/<region>/keyRings/<your-keyring-name>/cryptoKeys/<your-key-name>Retrieve it with:
gcloud kms keys describe <your-key-name> \ --project=<your-project-id> \ --location=<region> \ --keyring=<your-keyring-name> \ --format="value(name)"From the Console, open the key's details page and click Copy resource name.
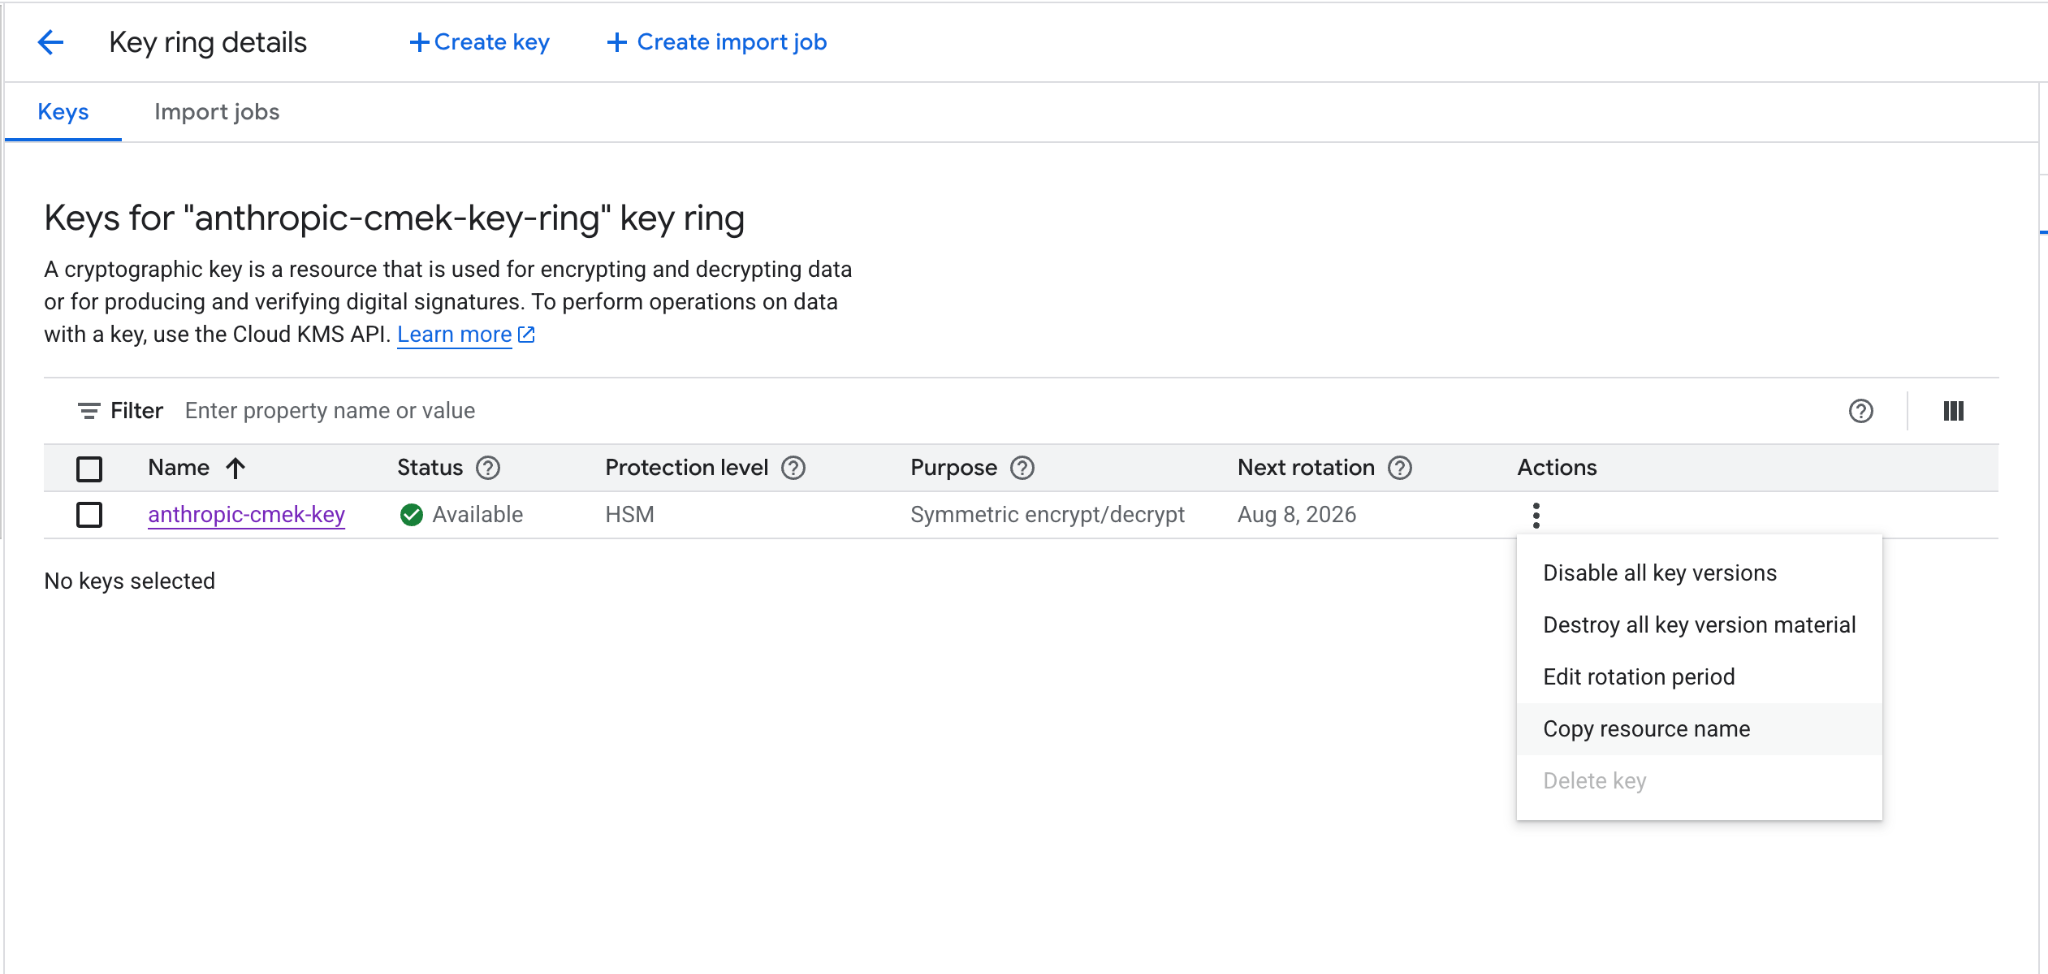
Copy the key's full resource name from the actions menu.
Register the key with Anthropic
How you register the key depends on which product you use.
You can set up the key in the Claude Console or through the Admin API, with the same result.
Register the key with Anthropic
In the Claude Console, open Settings > Encryption keys and click Add key. Enter a display name, choose Google Cloud KMS, and click Continue. Paste the full key resource name into Key resource name, and click Add.
Validate the key
On the Encryption keys page, click Verify next to the key. Connected appears when the check passes. If it fails, a message gives the reason.
Attach the key to a workspace
Open Settings > Workspaces, choose the workspace, and open its Security tab. Under Encryption key, select the key, click Save, and confirm. Attaching a key can't be undone. For a workspace that already receives requests, the key can take up to a day to take effect.
Terraform
For infrastructure-as-code deployments, the same steps map to the google provider with the google_kms_key_ring, google_kms_crypto_key, and google_kms_crypto_key_iam_member resources.
Was this page helpful?